← BACK TO THE LAB

DIGITAL FORENSICS / THE DISCIPLINE

Digital forensics.
Evidence in context.

Acquire carefully. Verify integrity. Correlate the artifacts. Explain what the evidence supports — and where it stops.

METHOD BEFORE CONCLUSIONS

Every finding
needs a foundation.

An artifact is a starting point. Its origin, timestamps, surrounding records and collection history give it meaning. A defensible investigation keeps those relationships intact.

Our research connects storage and device evidence with network context, evidence integrity and incident reconstruction. The emphasis is on a clear method and findings that another analyst can examine.

Read the original forensic research ↗
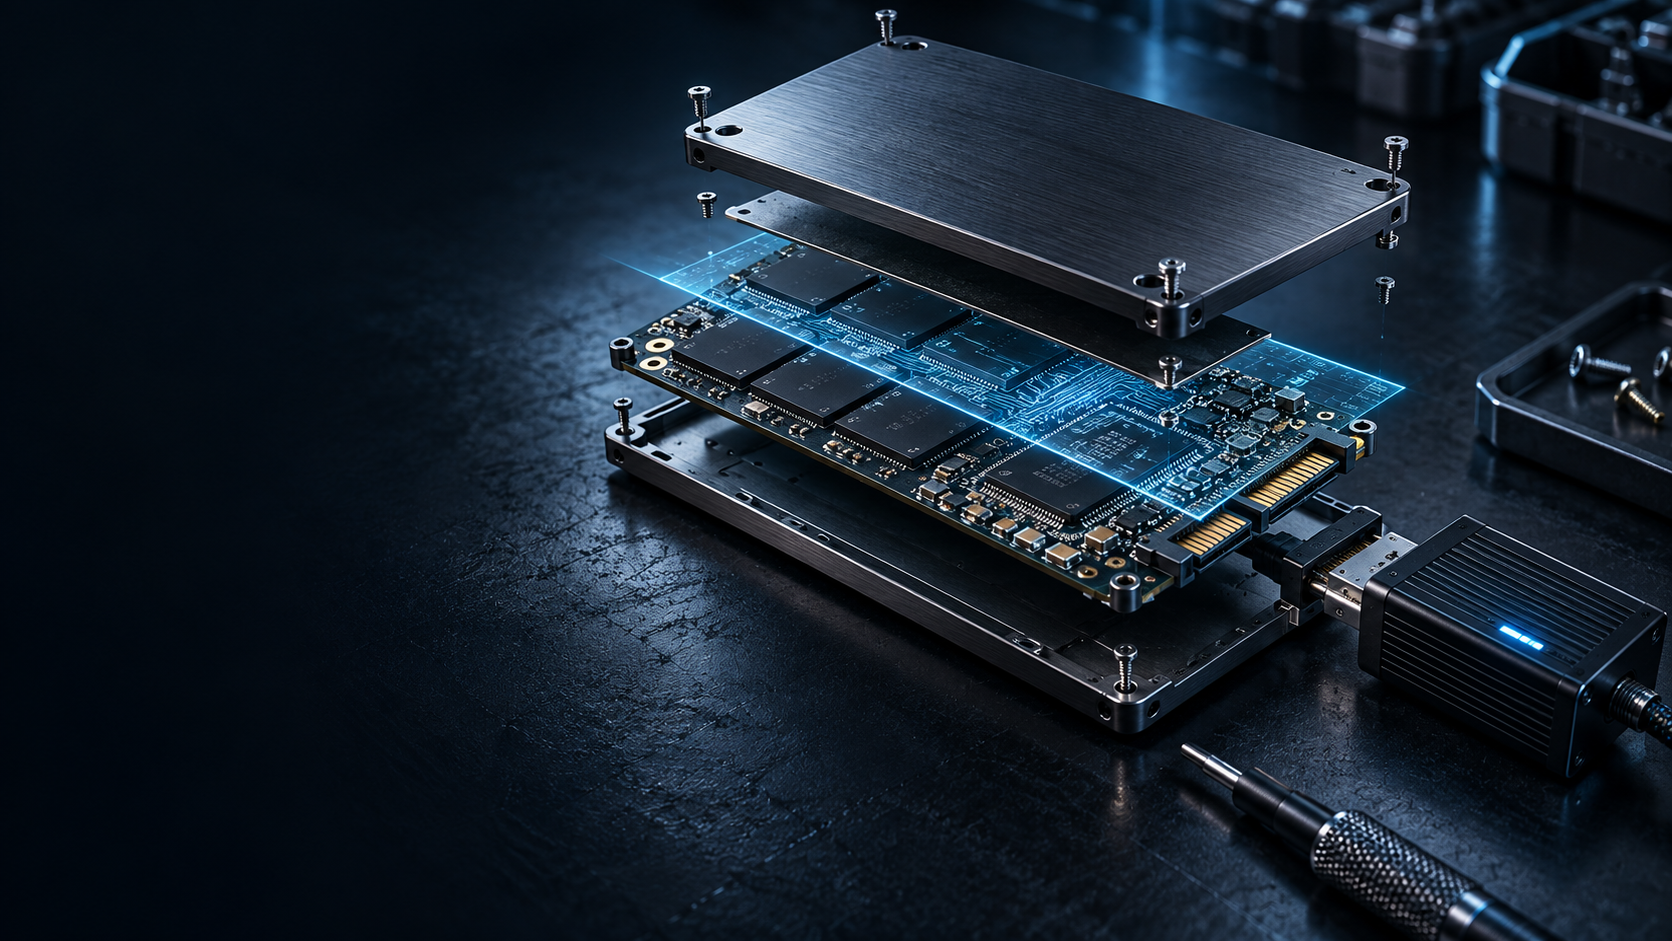
Exploded storage-device illustration showing the circuit board, enclosure and acquisition hardware

LOOK BEYOND THE SURFACE

Every byte.
In context.

The device is the beginning. A defensible finding connects the source, its artifacts and the limits of what they can tell us.

  1. 01

    Preserve the original.

    Document the source and the collection boundary.

  2. 02

    Verify the working copy.

    Keep integrity checks and the handling record together.

  3. 03

    Reconstruct with context.

    Correlate artifacts. Test alternative explanations.

Build an evidence timeline ↗
PRESERVE / VERIFY / EXPLAIN

FROM SOURCE TO FINDING

A disciplined investigation.

01 / ACQUISITION & PRESERVATION

Preserve the source.

Define the collection scope and record the condition of the source. Choose an acquisition method suited to the device, its state and the evidence sought. Keep original media separate from analysis and document every transfer.

Imaging & chain of custody ↗

02 / INTEGRITY & PROVENANCE

Make the handling traceable.

Record acquisition details, tool versions, identifiers and verification hashes. A matching hash supports byte-level consistency; the handling record explains where the evidence came from and what happened to it.

Evidence integrity in practice ↗

03 / ARTIFACTS & RECONSTRUCTION

Put the traces in context.

Correlate filesystem metadata, application records, device artifacts and network observations. Account for clock differences, missing records and alternative explanations. Distinguish an observed event from an inferred action.

Incident response foundations ↗

04 / FINDINGS & LIMITATIONS

Show how you got there.

Connect each finding to its supporting evidence. Explain the method, assumptions and uncertainty. Present a coherent timeline while keeping observations, interpretations and unresolved questions distinct.

Explore the forensic research ↗

KEEP INVESTIGATING

Research. Methods. News.

Explore the original field guides and research alongside the latest published articles. Digital forensics sits within a wider defensive practice: mobile hardening, private communications, containment and recovery all provide context.

Search the lab

NEWS / FORENSICS / FIELD GUIDES ESC