 websec
Findings and evidence
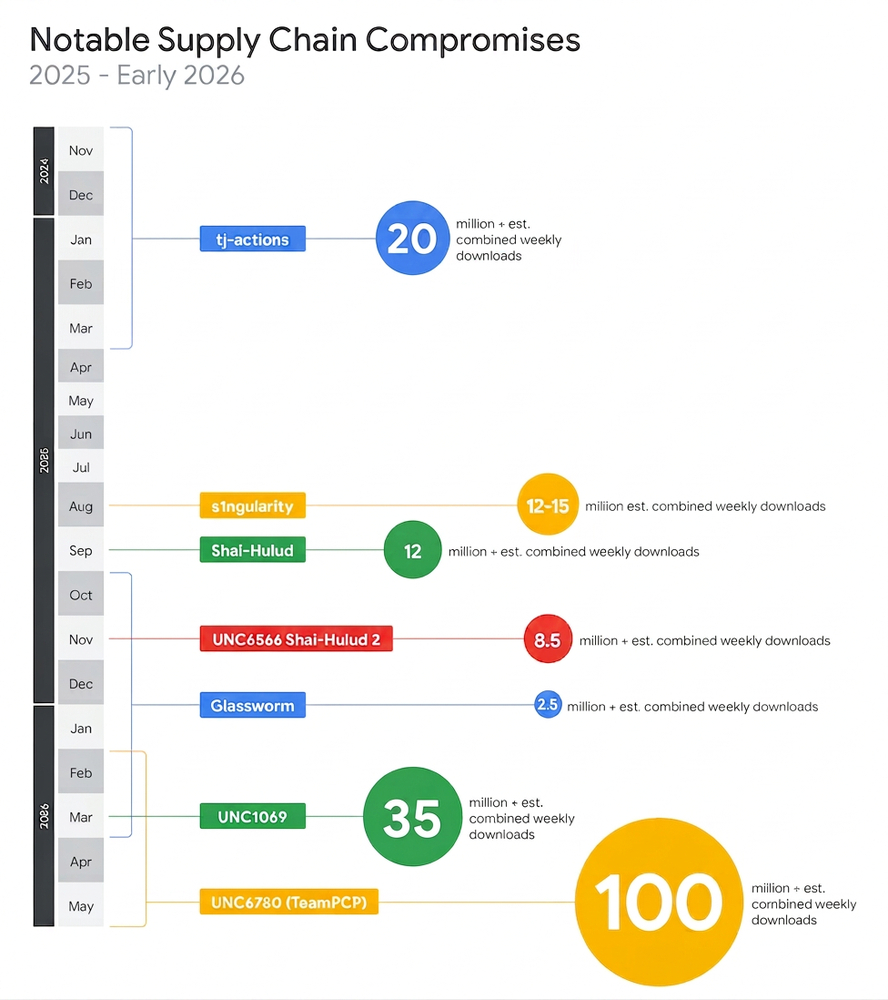
Google Threat Intelligence Group and Mandiant summarize observed growth in open-source supply-chain compromise. Their July publication draws on investigations involving repositories, dependencies and developer tooling, and discusses defensive controls across that lifecycle.
Why it matters
Preserve lockfiles, build provenance and dependency-resolution records so affected versions can be traced to actual deployments. An inventory becomes more useful when it connects a package to the systems that ran it.
Scope and limits
The selected incidents illustrate patterns in the researchers’ visibility. Package popularity alone cannot determine which installations were exposed or whether execution occurred.
Primary source
Google / Mandiant: original publication. Source published 2026-07-30. Brief prepared by websec.gr on 26 September 2026. This is an editorial research summary, not a claim of independent replication.